 LATEST
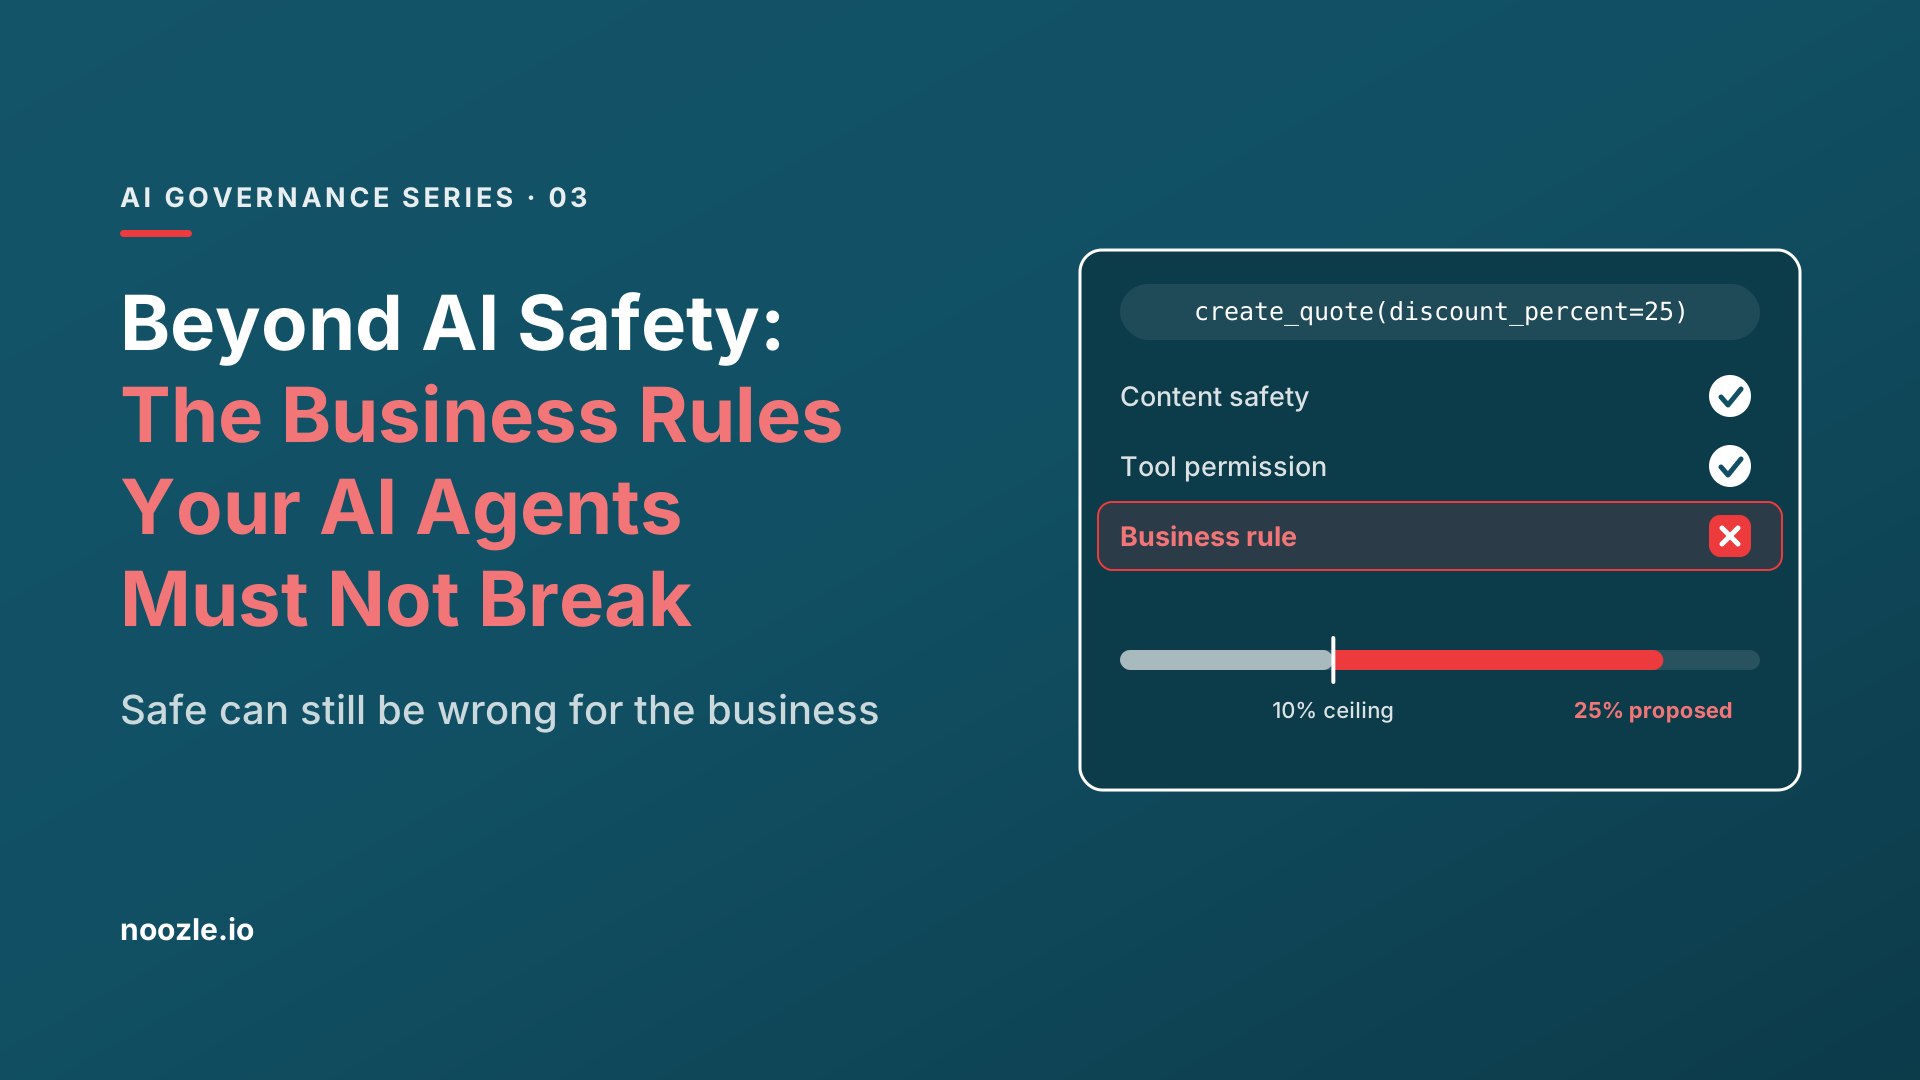
Beyond AI Safety: The Business Rules Your AI Agents Must Not Break
An AI agent can be safe, helpful and completely wrong for your business. Enterprises also need to enforce their own business rules.
Noozle Gate integrates with your AI gateway to enforce security and business policies across employee AI conversations and agent tool calls. Keep sensitive data within approved boundaries, with readable policies your team can audit and interactions you can trace.
Gate runs alongside your AI gateway, enforcing your policies across models from OpenAI, Anthropic, Google Gemini, DeepSeek and other providers. It checks requests before they reach the model and responses before they reach the user, so switching models doesn’t mean changing your rules.
Chat tools, internal apps and AI agents
One entry point for every model call
LiteLLM · full integrationHosted, EU-private or self-hosted models
Your policies, evaluated. EU cloud or on-premise.
IDs, policy revisions and outcomes, for your audit trail.
Streamed answers are checked as they flow.
Start LiteLLM with your provider credentials.
Connect Gate using the configuration supplied for your pilot.
Connect an app and verify an allowed request and a blocked request.
Using a different gateway? Tell us which one, and we will gladly integrate with it.Tell us your gateway
As your business grows, your policies grow with it. Gate’s highly optimized policy evaluation keeps AI interactions fast while applying your rules accurately. Your team can expand security controls and business rules with confidence in both speed and correctness.
team sales · model public-llm
“Draft a reply that beats the 18% discount Acme offered them.”
Gate checks every policy that could apply to this request, and only those.
7 could apply, checked in full · 1 match
Can’t apply · ruled out
and thousands more
Illustrative example.
An agent works through the same model calls as a person, only faster and without anyone watching. Gate checks every step it takes, so the rules you write for people also apply to your agents, along with rules written just for them.
Check the instructions and the context an agent starts from, for example which data a support agent may bring into a conversation.
Checked by GateDecide which tools each agent or team may be given. A support agent is never offered a payment tool.
Checked by GateCheck the actions the model asks the agent to take, including names and arguments, before they run. Stop a refund above a limit or a message to an outside address.
Checked before it runsApply rules to what tools return into the agent's context, such as documents and web pages, before the next model call.
Checked by GateThe result goes back to the model and the loop starts again. Gate checks every turn.
Gate decides on every agent step that passes through your AI gateway, while your tools keep running where they run today. Every stopped step is logged with the agent's identity, the policy and the revision.
Your team writes the rules, for security and for your own business, in one short and readable policy language. Every change creates a new revision. A privacy officer can read a policy, an auditor can review it, and every decision points back to the exact policy and revision that made it.
Patterns, fuzzy and proximity matching, and comparisons on any field of the request.matches · fuzzy · near
Language detection, lemmas and proper nouns, so a rule follows every form of a word.detect_language · lemma · propn
Multilingual similarity to a topic described in plain words, and key-passage extraction.about · about_score · textrank
Every rule can also use context: the key, team or user making the call, the model, the tools offered or called, and whether it is the request or the response. The bars show relative cost: semantic checks run only when cheaper conditions already hold.
Many LLM guardrails give you fixed categories to switch on or off, and when something is blocked you see a label and a score. With Gate every policy is yours: written in your words, adjustable down to the last condition, and explained on every decision.
Blocked · category personal_data · score 0.91
Fixed categories, a threshold, and a verdict you cannot open.
// Health data stays on EU-hosted models
!(doc.model startsWith "eu-private/")          your models
  && doc.request_data.team != "team-claims"   your exception
  && about(text, "patient diagnosis", 0.85)   your threshold
Blocked · health-topics-eu-only rev 7 · every condition traced
Every condition is readable, editable and versioned by your team.
| Can your team… | Typical guardrails | Noozle Gate |
|---|---|---|
| …read and change what a policy checks? | Usually a fixed category to switch on or off | Yes, every condition is yours |
| …see why a request was blocked? | Usually a category label and a score | Yes, the full reasoning with the matching text |
| …make exceptions ("everything except…")? | Usually left to a model to interpret | Yes, written into the rule |
| …match competitor or product names? | Usually described in words for a model to interpret | Yes: names, patterns, fuzzy matching |
| …depend on team, user, model and tools? | Usually set per configuration | Yes, in the same rule |
| …get the same decision for the same input? | Varies when a model is the judge | Yes, traced to a policy revision |
A category comparison. Individual products differ, and fixed categories are often quicker to switch on.
Manage Gate policies with the Noozle Terraform provider or the command line, in the same repositories and pipelines as the rest of your infrastructure.
noozle-cli, from a laptop or any CI job.resource "noozle_query" "health_eu_only" { name = "Health data stays on EU-hosted models" description = "Owned by compliance. Reviewed quarterly." full_expression = <<-EOT !(doc.model startsWith "eu-private/") && about(text, "patient diagnosis", 0.85) EOT tags = ["gdpr-art-9", "compliance"] is_active = true }
$ noozle-cli queries validate --expr-file health.expr
$ noozle-cli queries create \
    --name "Health data stays on EU-hosted models" \
    --expr-file health.expr --direction request
MATCH q:377 rev 4 request
Keep pricing and discount terms out of external AI
Query reasoning
AND
  metadata  request_data.team == "team-sales"    matched
  OR
    semantic  about(confidential discounts and commercial terms)   score 0.8712 / 0.8500
    regex     (floor price|discount)   skipped after ancestor short-circuit
  keyword   "Acme"   matched
Decision log: block, rule_match, q:377 rev 4Always. Every decision is logged with its policy and revision.
On demand. Open a trace session for a policy, for a limited time, and authorized people see the full reasoning, including the matching snippets. Traces are streamed live, straight to the people who asked for them.
The same product and the same policy language in both. Every pilot starts in the cloud, so you can try Gate before installing it yourself.
Every pilot starts here.
When you are ready to run it yourself.
Prompt and answer text, tool definitions and tool-call arguments. They are processed in memory and discarded.
Evaluation ID, policy and revision, outcome and completeness, model name, gateway call and trace IDs, timings.
Company data is flowing into AI. Sensitive data is at risk in both prompts and answers.
of employees regularly use AI on corporate devices.
2025 report: 15% Verizon DBIR, 2026data policy violations involving sensitive data sent to AI, in the average organisation.
2025: 44 per week Netskope AI Report, 2026data policy violations involving sensitive data returned by AI.
2025: 12 per week Netskope AI Report, 2026Relative increases within each source’s dataset, rounded to the nearest whole percent. Verizon compares its 2026 and 2025 reports; Netskope compares 2026 observations with 2025. Regular AI use means access at least once every 15 days.
Netskope also reports a sixfold increase in monthly prompts sent to generative AI apps.
Written policies set the rules; enforcement makes them hold. Nearly half of the privacy and security professionals surveyed by Cisco admit to entering personal or non-public data into GenAI tools (Cisco, 2025). Safety research points the same way. Aligned models can still be jailbroken (JailbreakBench), and detectors both miss attacks and block legitimate work (PIGuard, CAPTURE, GuardBench). That is the case for an independent layer, with rules you can read, that checks what goes in and what comes out.
Gate turns your compliance decisions into enforced, logged controls, and gives your DPO evidence for each one.
| Control | How Gate implements it | Supports |
|---|---|---|
| Personal data and identifiers | Pattern, fuzzy and semantic rules on prompts | GDPR Art. 5, 25, 32 |
| Special-category data | Multilingual topic rules by team and model | GDPR Art. 9 |
| Secrets and source code | Pattern rules on requests and responses | GDPR Art. 32 |
| Tool and agent use | Rules on tools offered and tool calls | OWASP LLM: excessive agency |
| Traceability | Decisions tied to policy revisions | AI Act Art. 12, 26 |
| Prompt injection | Rules on requests, answers and tool calls | AI Act Art. 15 · EDPS guidance |
Allow or block requests and responses. LiteLLM fully integrated; agentgateway, Kong AI Gateway and Bifrost in beta.
Deterministic, linguistic and multilingual semantic rules on text, tools, identity and model.
Privacy-safe decision records, dashboards and live policy tracing.
EU cloud and on-premise.
Describe a rule in plain words; Gate writes it as a readable policy you review, and explains every decision in plain words too.
Replace personal data with placeholders before the prompt leaves, and keep the rest of the request working.
Apply your rules to images in prompts and answers, not only to text.
Privacy, legal and business teams write, test and review policies in a web interface, with no code to learn.
Noozle is an Italian company, and your data stays under EU law, wherever your teams work. The team that wrote the policy language, the matching engine and the gateway integration is the team you talk to. Need a new kind of check? Tell us: we extend the product around what customers need.
Made
and hosted
in Europe
Route the events your business needs.
Gate checks your AI requests and responses. Streaming routes business events to the right destinations. Use the same policy language for both.
Follow one event from its source to every team and system that needs it.
See how Streaming routes eventsGuides, examples, and notes from Noozle.
LATESTAn AI agent can be safe, helpful and completely wrong for your business. Enterprises also need to enforce their own business rules.
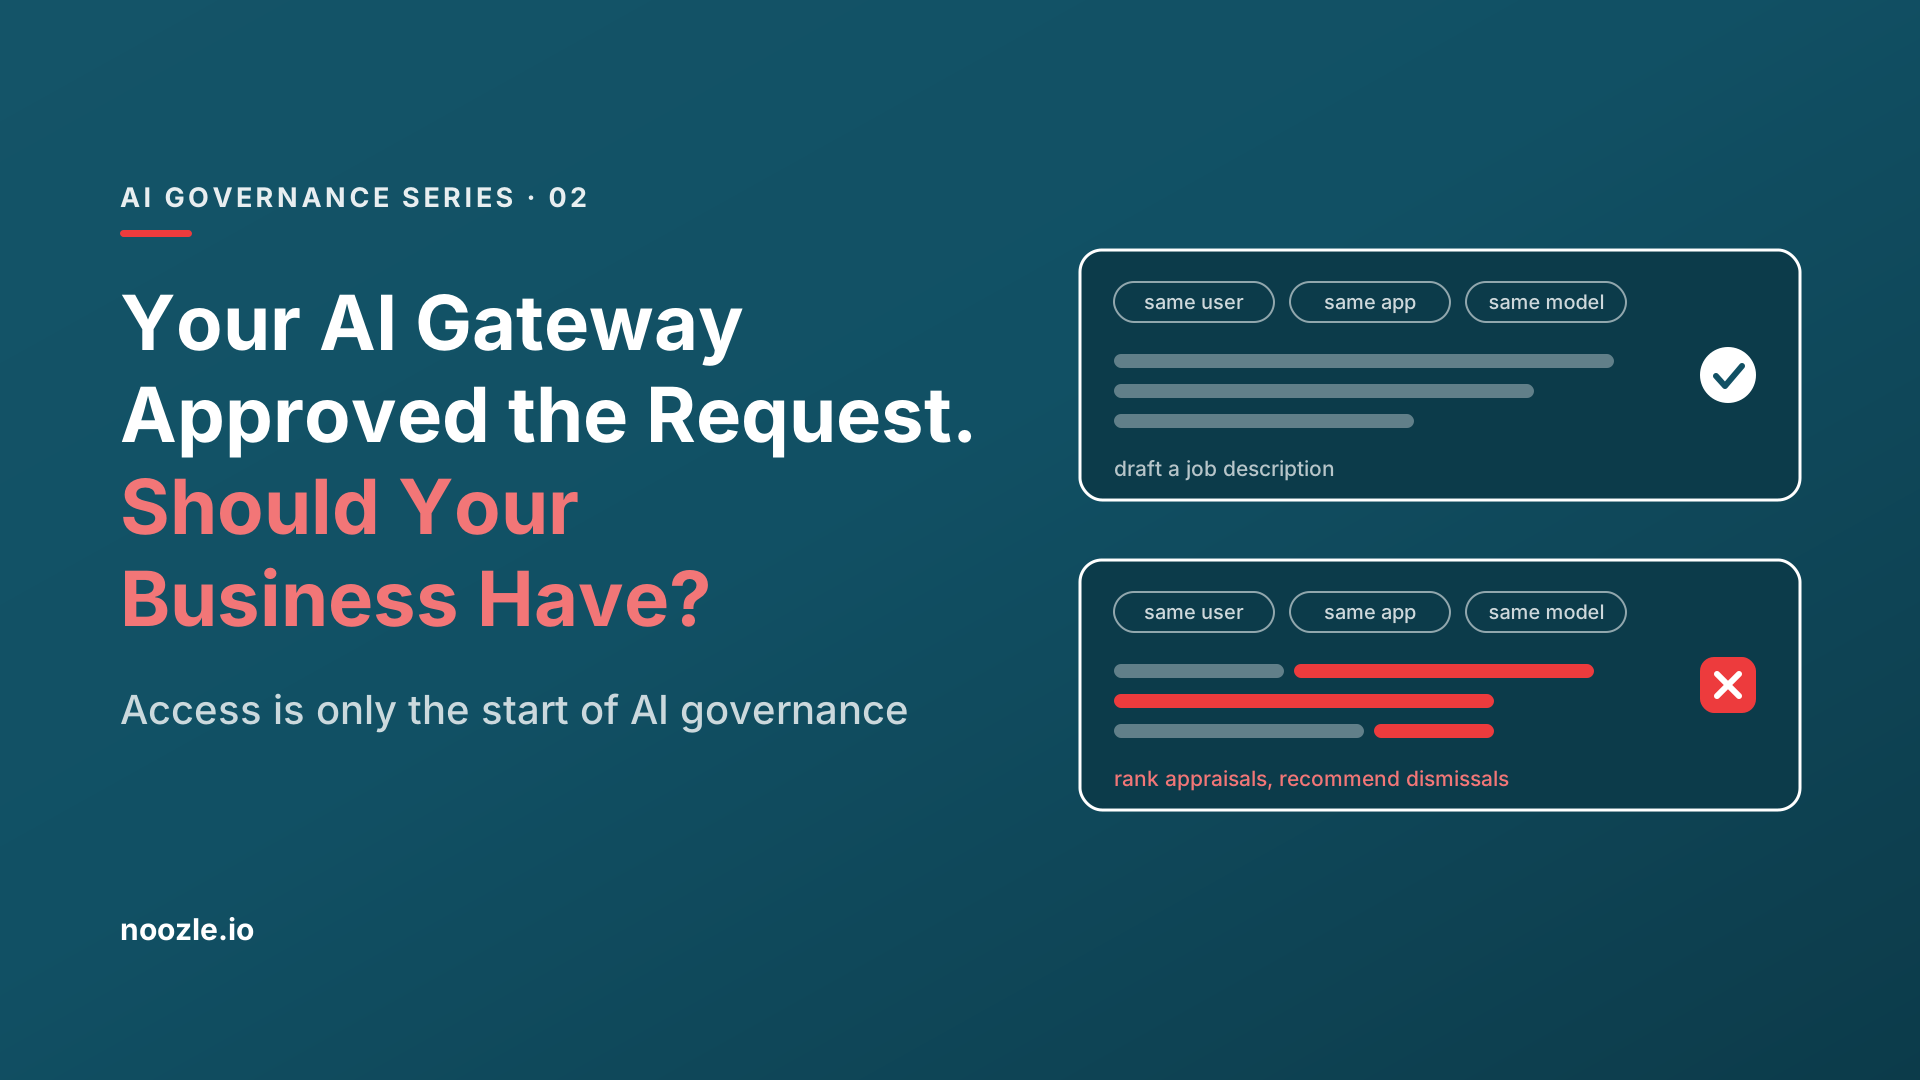
Why controlling access to AI models is only the beginning of enterprise AI governance.
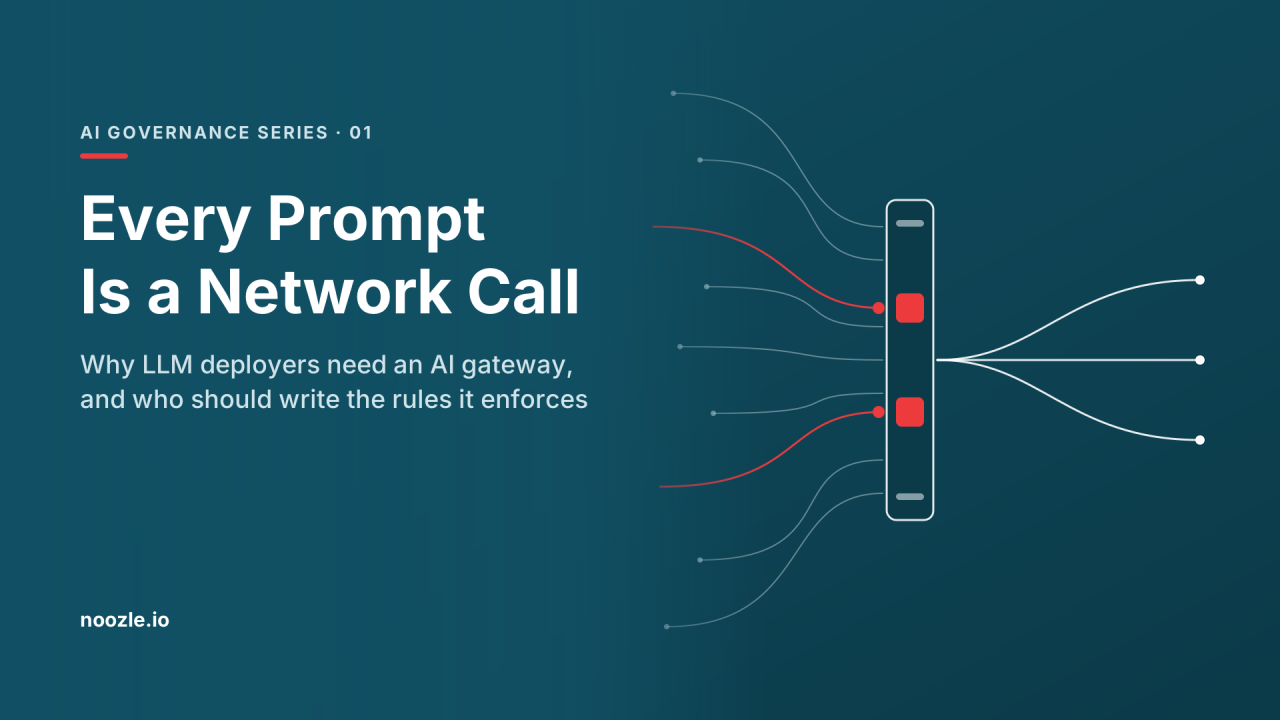
Why LLM deployers need an AI gateway, and who should write the rules it enforces.
Tell us what you want to control. We reply within 24 hours, usually sooner.
We map your LLM data flows and privacy risks with you.
Your first policies run in our EU cloud. Your privacy officer reviews the decisions.
Stay in the cloud, or move Gate into your own infrastructure.
Tell us which gateway you use and what you need to control. We reply within 24 hours, usually sooner.
We use your details only to reply to your request. Privacy policy.
Evaluating Noozle Gate or Noozle Streaming? Tell us which product you're interested in and what you need it to do. We're happy to answer questions about capabilities, integrations and deployment options.
Message received. Thank you for contacting Noozle. We’ll reply to your email address.